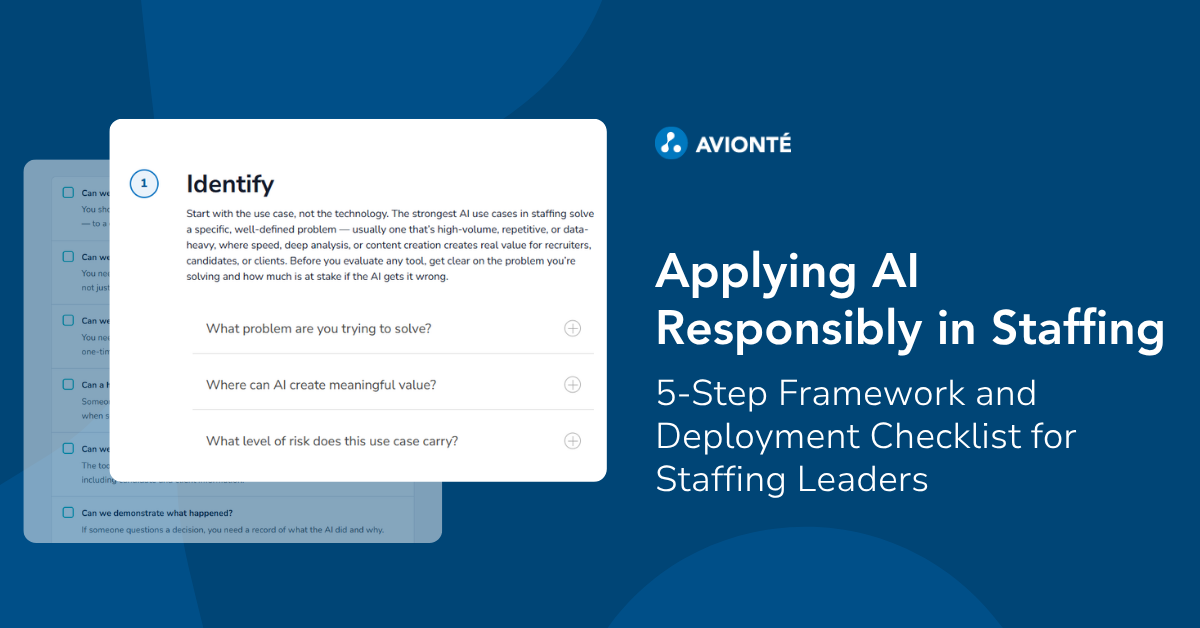
Applying AI Responsibly in Staffing
5-Step Framework & Deployment Checklist for Staffing Leaders
Download Here
Avionté protects the candidate, employee, and client data that staffing operations run on through layered controls, continuous monitoring, independent assessments, and documented recovery procedures.
SOC 2 Type II
Independent attestation covering Security, Availability, and Privacy.
24 / 7 / 365
A managed security operations center monitors, hunts threats, and supports incident response.
25+ Policies
Security and privacy policies, each reviewed annually.
100% Cloud-Native
No on-premises data centers or colocation facilities.
Staffing operations handle sensitive candidate, employee, and client information every day. These controls protect it across six areas.
Encryption at rest, in transit, and on company-managed endpoint disks. Role-based access, logged privileged access, single sign-on, and multi-factor authentication.
A third-party security operations center monitors, hunts threats, and supports incident response 24/7/365. Endpoint detection and response, centralized logging, data loss prevention, and a documented incident response plan with customer notification procedures.
A web application firewall, DDoS protection, and continuous vulnerability scanning. Code is analyzed, tested, and peer reviewed before release.
No on-premises data centers. Production runs on AWS, with select supporting services on other cloud providers. Backups are encrypted and replicated across regions, with recovery runbooks for every critical system.
Practices aligned to CCPA/CPRA, GDPR, PIPEDA, and biometric privacy requirements. A designated executive owns privacy, and a defined process handles personal data requests.
An executive-approved AI Security Policy and an inventory of approved AI tools and use cases, with data loss prevention controls on AI prompts.
Written policies set the rules the security program follows.
The CTO is accountable for the security and privacy programs, supported by a dedicated security team and a cross-functional Security Guild.
Controls are reviewed on a regular schedule, including ongoing monitoring, periodic access reviews, and annual reviews of assessments, privacy, and AI governance.
Every year, outside firms test and assess Avionté’s security. Penetration test findings are tracked through remediation and retest.
| Assessment | Frequency | Scope and result |
|---|---|---|
| SOC 2 Type II examination | Annual | Covers Avionté’s controls for Security, Availability, and Privacy. Avionté has been attested for consecutive annual periods since 2022, and the current report is available on request. |
| Third-party security audit | Annual | An independent firm assesses the full control program. |
| Penetration testing | Annual | A third party tests applications and the external perimeter. Findings are tracked through remediation and retest. |
| Independent risk assessment | Annual | An independent reviewer assesses governance, controls, and security hygiene. |
| Payments (PCI) | Ongoing | Payments run through a PCI-compliant third party. Avionté stores no cardholder data. |
| Framework alignment | Ongoing | Program aligned to ISO 27001, the NIST Cybersecurity Framework, and CIS Controls. SOC 2 controls are mapped to ISO 27001. |
Yes. The platform is cloud-native, and updates are delivered to every customer without on-premises installs.
Production runs on AWS, with select supporting services on other cloud providers.
Avionté provides its SOC 2 Type II report and supporting security documentation on request. Email security@avionte.com or use this form.
Through automated tooling under the Patch Management Policy, with timelines based on risk and severity.
Payments run through a PCI-compliant third party, and Avionté stores no cardholder data.
Yes. Avionté carries cyber insurance, and certificates are available on request.
WorkN is now Avionté Mobile. Building on the power and functionality of WorkN’s talent mobile app, Avionté Mobile is built for the high-volume staffing and recruiting industry.